Application security testing for UAE businesses
Find the weaknesses before an attacker does. We test your web applications, APIs and mobile apps the way a real attacker would approach them, explain what we found in terms of business risk, and help your developers fix it.
Penetration testing, API and mobile app security testing, secure code review, cloud configuration review and remediation support, from a team that builds software as well as testing it.
Coverage and services
What application security testing is, and why it matters
Application security testing looks for the ways your own software can be misused: a login that can be bypassed, an API that returns another customer's data, a mobile app that stores a password in plain text. Firewalls and antivirus do not see these, because the application is working exactly as it was written.
- What gets tested The parts of the system an outsider can reach — web pages, APIs, mobile apps, browser extensions — and the code and cloud configuration behind them.
- How it differs from a scan Automated scanners find known patterns. Broken authorization, business logic flaws and small weaknesses chained together need a person who understands what the application is meant to do.
- What OWASP has to do with it OWASP publishes the most widely used lists of web, API and mobile risks and the verification standards that go with them. We use them as a baseline for coverage, then test what is specific to your application.
- Why it is not a one-off A clean report describes the code on the day it was tested. New features, new dependencies and new configuration change the picture, so testing follows significant releases.
Business challenges we solve
Six reasons businesses come to us about application security — often after a customer, a partner or an incident asked a question nobody could answer.
A security questionnaire you cannot answer
A large customer or partner wants evidence of security testing before signing, and there has never been an independent test of the application.
APIs that trust too much
The mobile app and partners call APIs that check who is logged in but not what they are allowed to see, so one customer's ID unlocks another's data.
Mobile apps carrying secrets
Keys, tokens and personal data stored on the device or built into the app, where anyone who downloads it can extract them.
Code written fast, never reviewed
Features shipped against deadlines with no security review, on dependencies nobody has updated since the project started.
Cloud storage open to the internet
Buckets, databases and admin panels reachable from anywhere because a default setting was never changed.
A scan report nobody can act on
An automated tool produced hundreds of findings with no priority, half of them false alarms, and the team does not know where to start.
Our application security services
Five services covering how an application is attacked, and what it takes to close the gaps afterwards.
Web application penetration testing
Hands-on testing of your web application the way an attacker would approach it.
Authentication, sessions, access control, injection, business logic and the OWASP Top 10, with tooling and manual analysis.
API security assessment
Your APIs tested for who can call them, what they return and what they can be made to do.
REST and GraphQL APIs, object-level and function-level authorization, rate limits and data exposure, against the OWASP API Top 10.
Mobile app security testing
Android and iOS apps tested on the device and against the back end they talk to.
Local data storage, secrets in the app package, network traffic, authentication and platform settings, using OWASP MASVS.
Secure code review
Your source code read for the vulnerabilities testing from the outside can miss.
Manual review of high-risk code, static analysis, third-party dependency checks and secrets left in repositories.
Remediation and hardening
Help closing what we found, not only a list of it.
Fix guidance with your developers, encryption and access controls, WAF and cloud configuration, then retesting.
What we test
Twelve areas across four layers of an application. A first assessment usually covers the parts exposed to the internet, then moves inward to the code and the cloud setup behind them.
Applications and APIs
Everything a user, a partner or an attacker can reach.
Web applications
Customer portals, admin panels and internal tools, signed in and signed out.
APIs
Public, partner and internal APIs, including the ones only your own apps are meant to call.
Browser extensions
Plugins checked for excess permissions, data leakage and unsafe communication.
Mobile
Apps that run on hardware you do not control.
Android apps
App package, local storage, inter-app communication and platform settings.
iOS apps
Keychain and file storage, transport security, and what the binary gives away.
Mobile back ends
The APIs and services behind the app, tested as an attacker with the app in hand would.
Code and dependencies
Where most vulnerabilities are written in the first place.
Source code
High-risk paths read by hand: authentication, payments, file handling and data access.
Third-party libraries
Dependencies checked for known vulnerabilities and abandoned packages.
Secrets in code
Keys, passwords and tokens found in repositories, history and build pipelines.
Cloud and hosting
The configuration around the application.
Cloud configuration
Storage, databases, identity roles and network exposure reviewed against least privilege.
WAF and CDN setup
Web application firewall rules and edge settings checked for gaps and bypasses.
Security logging
Whether a login attack or data export would be recorded, and whether anyone would be told.
Security testing in the UAE regulatory context
The attacks are the same everywhere. What differs in the UAE is which laws and standards a finding relates to. We map findings to them to help you prepare; the legal reading stays with your advisers.
The federal data protection law
Federal Decree Law No. 45 of 2021 Regarding the Protection of Personal Data governs how personal data is handled. Our findings show where your application exposes it, so you can prioritize those fixes.
Where personal data travels
The same law sets requirements for cross-border transfer. We trace which third-party services, analytics tools and regions your application actually sends personal data to.
UAE Information Assurance Regulation
TDRA's regulation is mandatory for entities it designates as critical and recommended for everyone else. We help align application controls and evidence with its requirements.
DIFC and ADGM
Businesses in these free zones have their own regimes: DIFC Law No. 5 of 2020 and the ADGM Data Protection Regulations 2021. We work from whichever your advisers confirm applies.
Health data
Federal Law No. 2 of 2019 on the use of ICT in health fields applies across the UAE, including free zones. Healthcare applications are scoped with that law in mind.
Copies outside the country
Data hosted in a UAE region can still have backups, logs or replicas elsewhere. The cloud configuration review checks where those copies actually go.
Application security testing process
Six stages on every engagement. Nothing is tested until scope and rules of engagement are agreed in writing, and nothing ends until the fixes have been retested.
-
Scope and rules of engagement
What is in scope, which environments, which accounts and which hours — agreed and signed off before any testing starts.
-
Threat modeling
We map how a realistic attacker would approach your application, so testing concentrates on the paths that carry real risk.
-
Assessment and testing
Hands-on testing across the agreed scope, combining tools with manual analysis, with anything critical reported to you immediately.
-
Reporting
Findings with severity, reproduction steps and business impact, and a summary leadership can act on without reading the technical detail.
-
Remediation support
We work through the fixes with your developers, or make them ourselves where that is agreed.
-
Retest and follow-up
Every fix retested to confirm it holds and has not introduced something new, then a plan for when to test again.
Why choose Techwaresoft for application security?
Seven things that follow from being a software company that tests security, rather than a scanning service that hands over a report.
Findings your developers can fix
We build applications ourselves, so each finding comes with a fix your developers can apply in their own framework and code — not a generic recommendation copied from a scanner's library.
Manual testing, not only tools
Scanners are the starting point; business logic and access flaws need a person.
Prioritized by business risk
Your team knows what to fix first instead of facing an unranked list.
Retesting included
Fixes are checked, so the report you keep reflects the application after remediation.
No surprises in production
Anything that could disrupt a live system is agreed in advance, or tested on staging.
Based in the UAE
A Sharjah team familiar with the UAE's data protection and assurance landscape.
Reports for two audiences
A summary for leadership and technical detail for the people doing the fixing.
Trusted by
A launch hosted behind a WAF and CDN
Our published case with application protection in it: a Dubai catering brand's Odoo website, brand and social launch, hosted behind a web application firewall and CDN. It was a launch project rather than a security assessment, and an application security case study will take its place once a client has approved one.
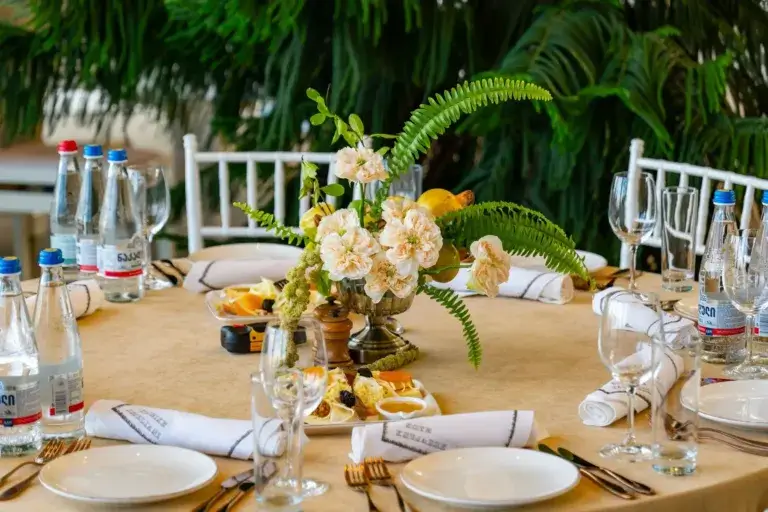
From ground zero to gourmet — a digital launch for a luxury catering brand
- Challenge
- A Dubai catering company with a premium offline reputation and nothing digital — no website, no identity, no sales assets — on a launch deadline.
- Solution
- An Odoo site with a menu the team edits itself, a full brand identity and shoot, social launch on Instagram, Facebook and TikTok, and hosting behind a WAF and CDN.
- Result
- Within 90 days — a surge in organic and social traffic, and high-value enquiries from event planners and private clients.
- Odoo
- Managed hosting
- Brand & social
Industries we serve
The testing methods are the same in every sector. What changes is what an attacker would be after, and which rules apply to the data they could reach.
Finance & FinTech
Payment flows, account access and transaction APIs, where a logic flaw is a direct financial loss.
Talk to us
Healthcare
Patient portals and apps holding sensitive records, tested for who can reach which data.
Talk to us
Retail & Ecommerce
Checkout, customer accounts, coupons and stored addresses — common targets for account takeover and abuse.
Talk to us
Technology & SaaS
Multi-tenant platforms where one customer must never see another's data, and enterprise buyers ask for proof.
Talk to us
Education
Student records, exam systems and parent apps used by young people on shared devices.
Talk to us
Recruitment & HR
CVs, passports and salary details uploaded and stored at volume, behind portals open to the public.
Talk to us
Real Estate
Tenant and buyer documents, payment links and agent portals shared across many outside users.
Talk to usWhat clients say about working with us
Clients on how the delivery went. None of these is a security engagement; a security-specific testimonial will replace the first once a client has approved one.
They built software that truly matched our needs. The team was responsive, detail oriented, and reliable, delivering solutions on time and ensuring the quality exceeded what we had hoped for.
Techwaresoft's staff augmentation transformed our team. Their skilled professionals integrated seamlessly into our projects, bringing reliability, expertise, and efficiency. The team's proactive approach ensured our deadlines were met while elevating overall project quality.
Techwaresoft built a learning platform that is intuitive and engaging. The design makes learning drums enjoyable and straightforward, and their attention to user experience really stands out. Our students love the platform.
Frequently asked questions
The things businesses ask before commissioning a security test. If yours is not here, it is the fastest thing to answer in a conversation.
How is this different from an automated scan?
Scanners find known patterns. They do not find broken authorization, business logic flaws or chained weaknesses, which is where real breaches usually start. We use tools as a starting point, not as the assessment.
Will testing disrupt our live environment?
Testing is scoped and scheduled with you, and where risk to production is a concern we test against a staging environment. Anything potentially disruptive is agreed in advance, never a surprise.
How often should applications be tested?
At minimum after significant changes to authentication, payments or data handling, and periodically beyond that. Applications drift, and a clean report describes the code as it was on the day.
Do you test against the OWASP Top 10?
Yes, as a baseline, along with the OWASP API Security Top 10 and the mobile standard, MASVS, where they apply. The OWASP lists cover common risks; we also test what is specific to how your application works.
Will this make us compliant with UAE data protection law?
Testing alone cannot make an organization compliant. It shows where your application could expose personal data and gives you evidence of the controls in place, which helps you and your advisers prepare.
Do you need our source code?
Not for a penetration test, which can be run from the outside. Access to the code makes a test more thorough, and it is required for a secure code review.
What do we receive at the end?
A report written for two audiences: a summary your leadership can act on, and technical detail with reproduction steps your developers can work from directly. Retesting confirms the fixes.
Find the weaknesses before someone else does
Tell us what your application does, who uses it and what data it holds. We will tell you what to test first, how deeply, and what it takes to close what we find.
A first call is about your application and its risks rather than tools: what an attacker would want from it, who can reach it, and what has changed since it was last tested.